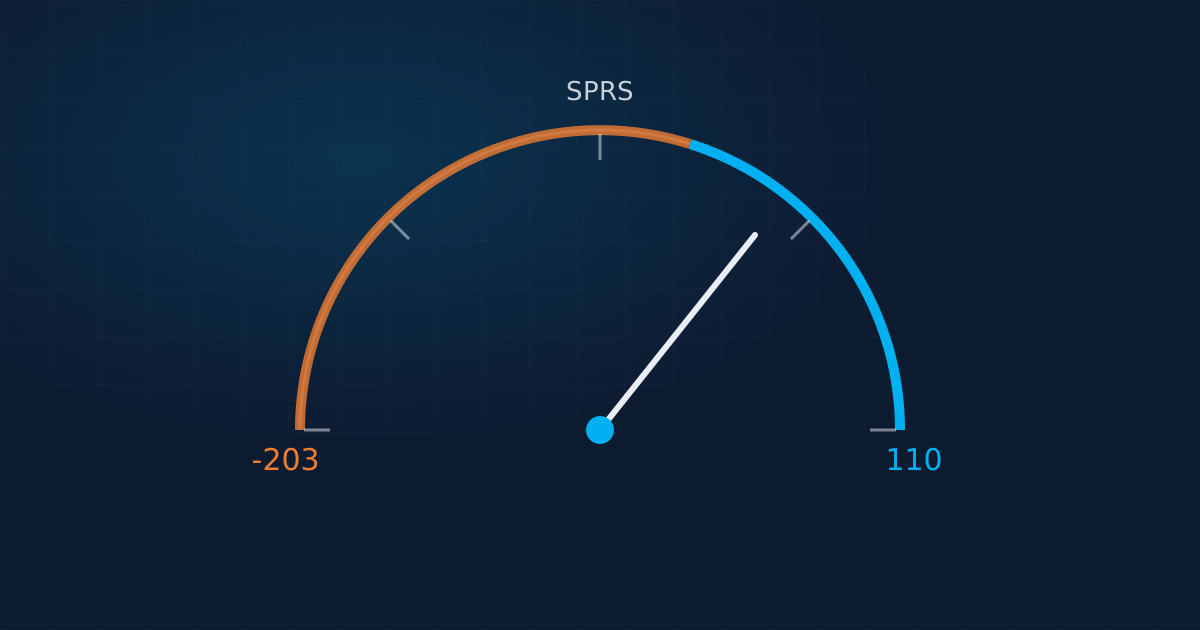
Where the number comes from
The DoD Assessment Methodology scores your implementation of NIST SP 800-171 Rev. 2. You start at 110, one point for each requirement, and subtract a weighted penalty for every requirement you haven't fully implemented.
The penalties are weighted by risk. Each unimplemented requirement costs 5, 3, or 1 points: five for the controls whose absence exposes the whole environment (multifactor authentication or boundary protection, for example), three for controls with a specific but serious exposure, and one for the rest.
Across all 110 requirements the deductions add up to 313, so a company with nothing implemented lands at 110 − 313 = −203. A negative score is simply what that arithmetic produces once enough weighted gaps are open. Most contractors' first honest self-assessment lands somewhere between −100 and +50.
Two controls get partial credit; one has no point value
- 3.5.3 (MFA): if you've deployed multifactor for remote and privileged access but not yet for general users, you lose 3 points instead of 5.
- 3.13.11 (FIPS-validated cryptography): if you encrypt CUI but the modules aren't FIPS-validated, you lose 3 points instead of 5.
- 3.12.4 (System Security Plan): there is no point value here, because without an SSP you are not eligible for a score at all. The methodology treats a missing SSP as a finding that "an assessment could not be completed."
Why honesty beats optimism
Your SPRS submission is a representation to the federal government, and the Department of Justice has already pursued False Claims Act cases over inflated cybersecurity attestations. An honest −40 with a dated plan of action is a defensible business position, while a hopeful 110 you can't evidence is a liability with your signature on it.
There's a practical reason too. Under the CMMC phase-in that began November 10, 2025, applicable new awards require a current CMMC self-assessment result in SPRS, with an affirmation. Primes read those scores, and a credible number that is visibly improving reads far better than a perfect one that collapses under diligence.
Raising the score fastest
Because the weights are lopsided, the order of the work matters more than the amount of it. This is the pattern we see across engagements:
| Move | Typical gaps closed | Points recovered |
|---|---|---|
| MFA everywhere (Entra ID conditional access) | 3.5.3 and related access controls | 5-15 |
| FIPS-validated encryption for CUI at rest / in transit | 3.13.11, 3.13.8, 3.8.6 | 9-15 |
| Centralized logging + alerting (Sentinel) | 3.3.x audit family | 8-14 |
| Boundary + segmentation cleanup | 3.13.1, 3.13.5, 3.1.3 | 10-15 |
Before any of that, shrink the boundary. Every control you implement applies to everything in scope, so reducing scope first makes every later point cheaper. Our CUI Scope Reduction Field Guide explains how.
The free CMMC Calculator will do the arithmetic for you. It scores all 110 controls with the official DoD weights, ranks your points at risk by impact, and builds a remediation scenario with real timelines.
Want your score validated before a prime asks for it?
A practitioner will review your self-assessment, flag the scores that wouldn't survive scrutiny, and hand you a sequenced path to a number you can sign. Or email rj@indirectit.com directly.